
01
Observe
Capture hostile activity from honeypots and protected systems while retaining the evidence surrounding each event.
Pynblok analyses hostile activity, enriches the evidence and identifies the infrastructure behind attacks.
The aim is simple: move beyond the individual IP address and build a better understanding of the networks, systems and behaviour associated with hostile activity.
A traditional blocklist asks a relatively simple question: should this address be blocked?
Pynblok takes a broader view. It gathers evidence from hostile activity and combines it with information about networks, geography, autonomous systems, behaviour and previous observations.
This creates a picture of the infrastructure behind the activity — allowing defensive decisions to be based on intelligence rather than an isolated event.
Pynblok turns observations into intelligence that can be examined, understood and acted upon.
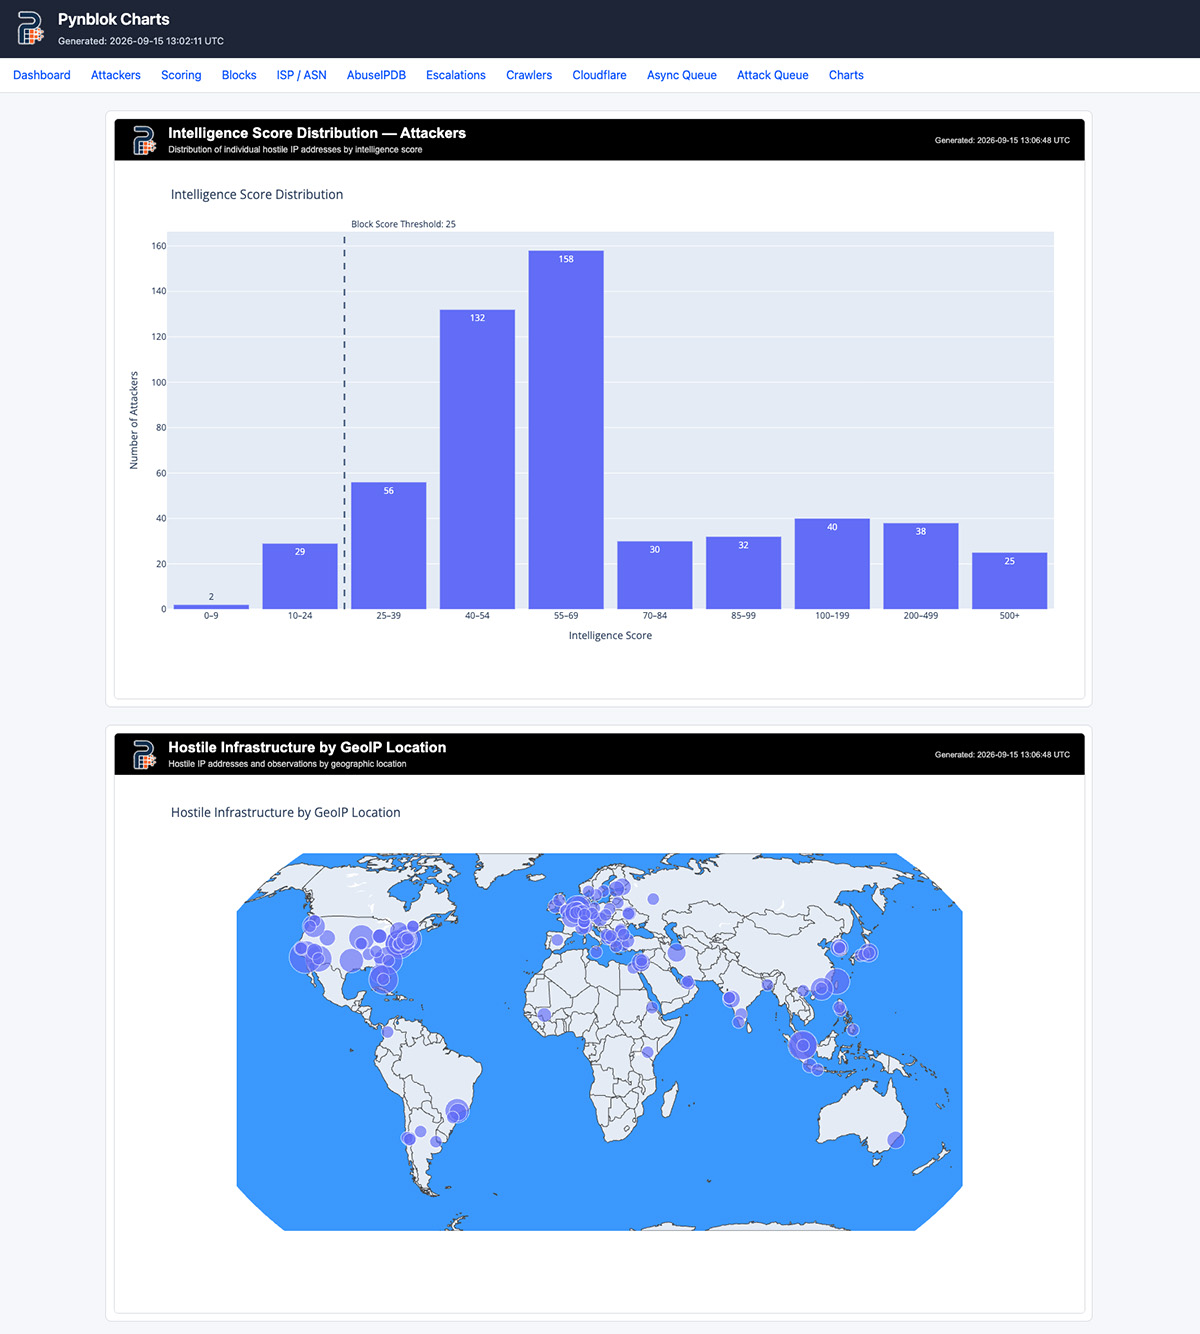
Capture hostile activity from honeypots and protected systems while retaining the evidence surrounding each event.
Enrich observations with network, geographic and behavioural information and classify the activity.
Convert accumulated intelligence into defensive decisions and automated network protection.
Don't just block the attacker.
Understand the infrastructure behind the attack.